Private services, reachable from cloud agents
Capy machines join your tailnet as tagged, ephemeral nodes, so agents reach the internal databases and APIs your tailnet policy grants them. Your private services stay off the public internet.


Connect in four steps
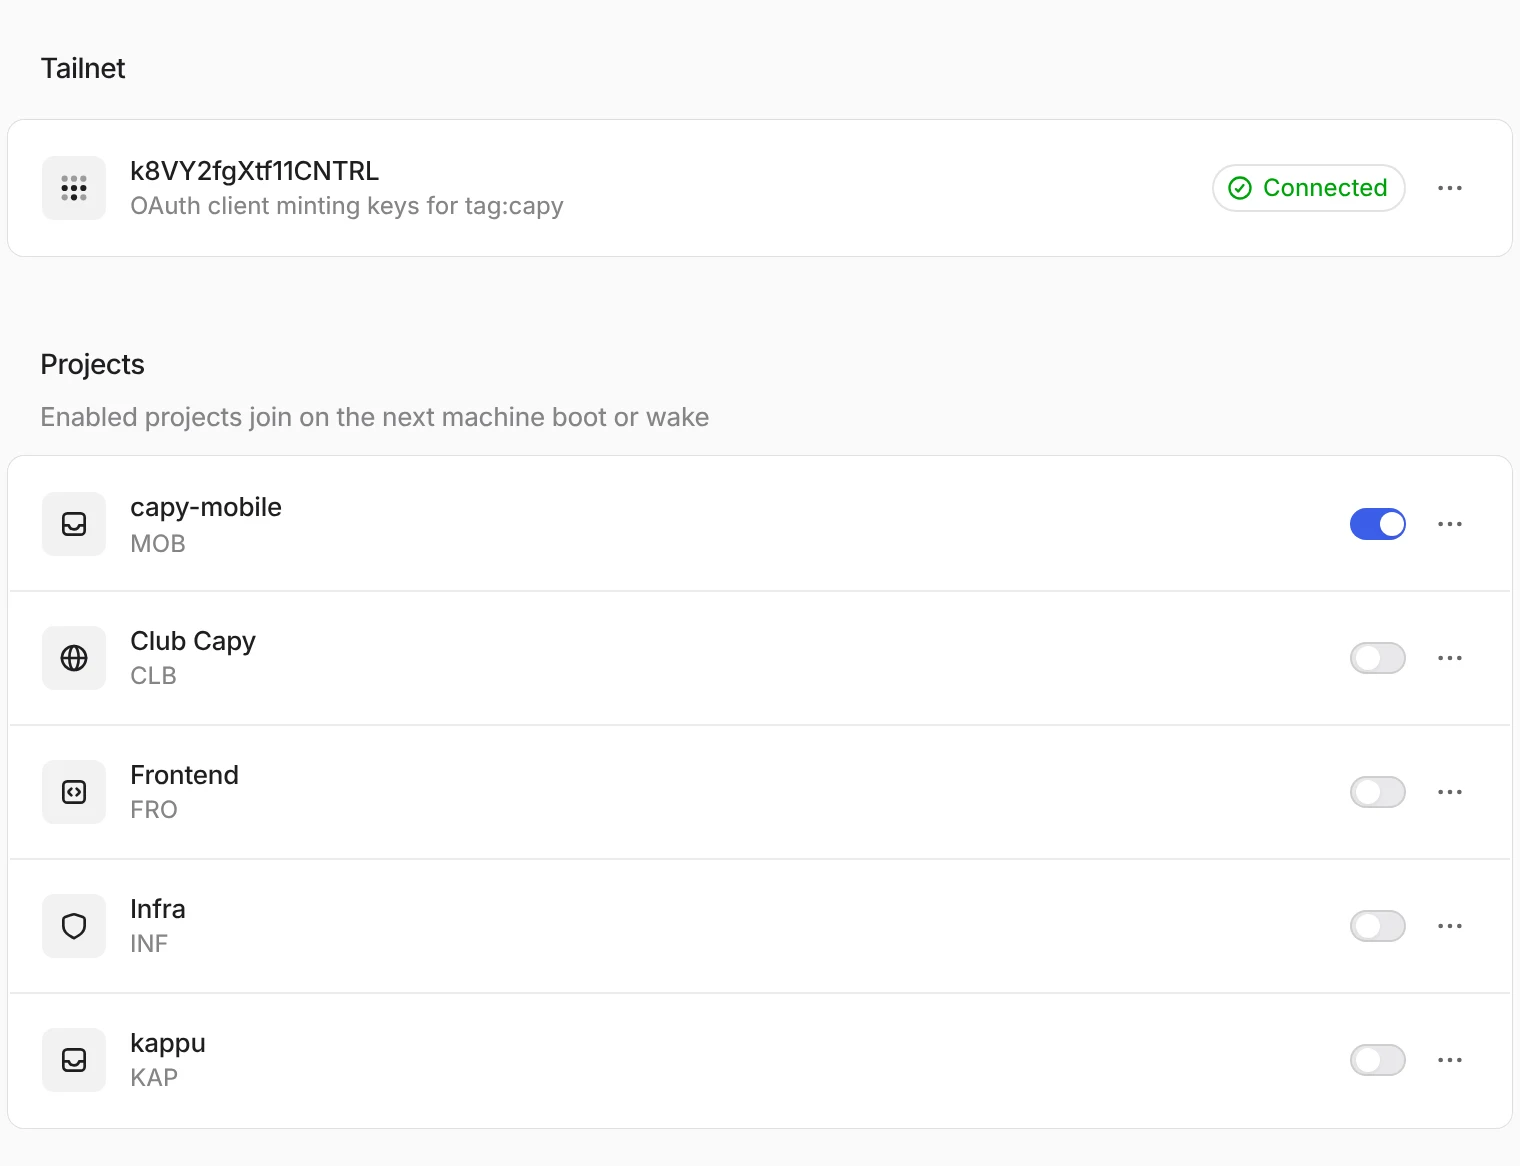
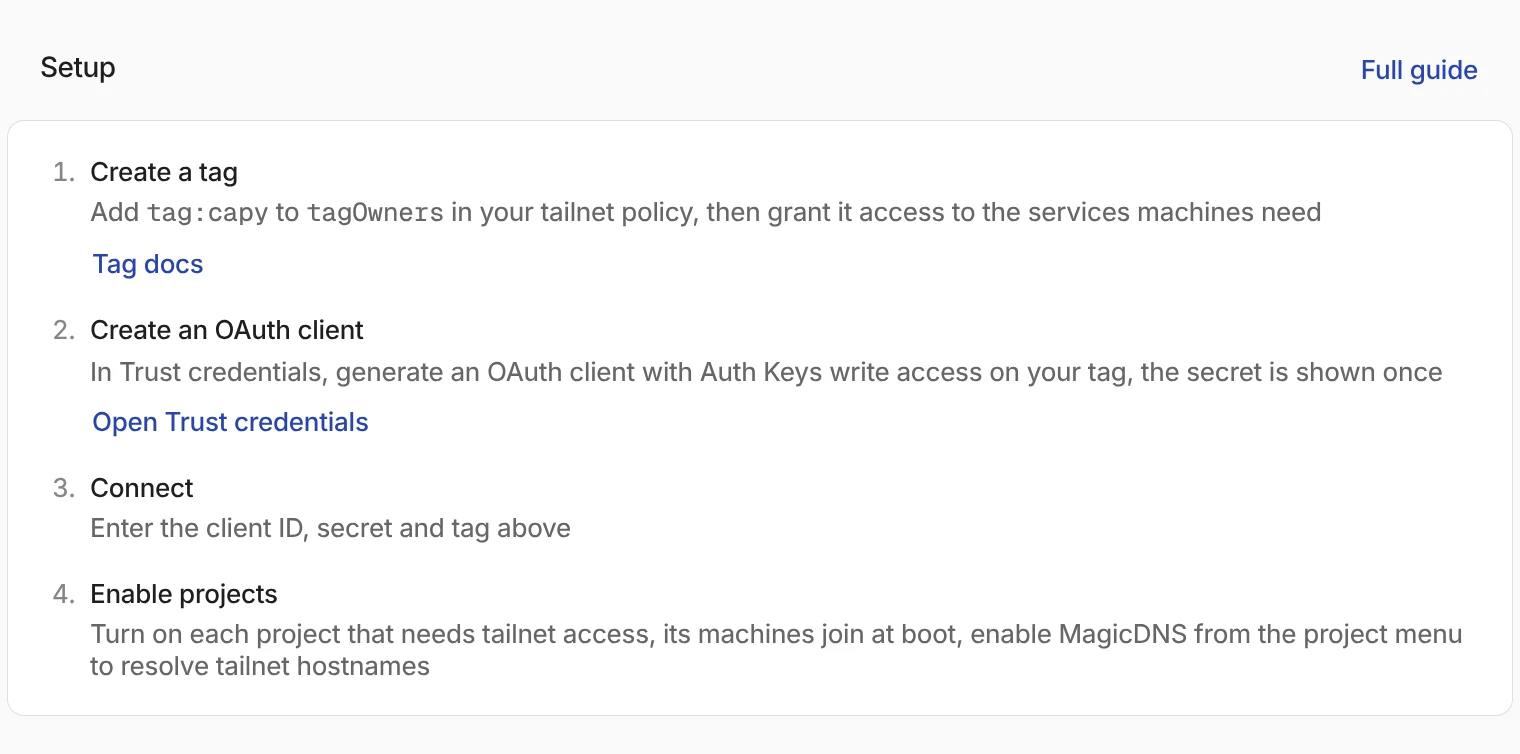
Add a tag to your tailnet policy, create an OAuth client that can only write auth keys for it, connect it in Capy, and pick the projects whose machines join.
Read the setup guide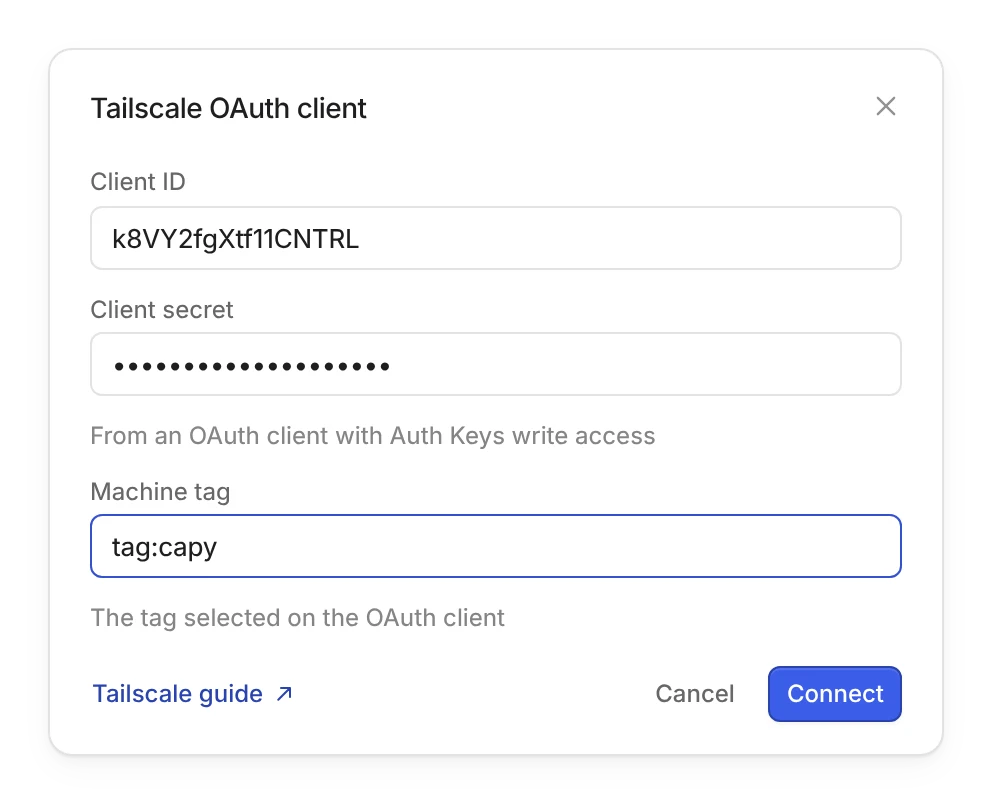
One narrow scope
The OAuth client needs only Auth Keys write on your tag. Capy checks it against your tailnet before saving.
Steps in the app
Capy’s Tailscale page lists each step, with links to the tag docs and Trust credentials.
Only what your policy grants
Machines carry the tag you chose and reach only what your tailnet policy grants that tag. Scope that tag’s rules to the services agents need.
Tagged, short-lived nodes
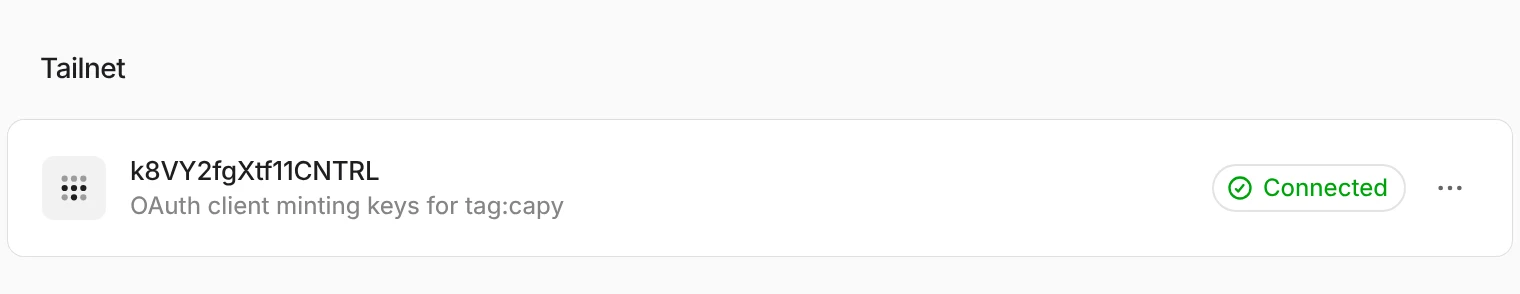
Each join uses a single-use key that expires after five minutes. Tailscale removes the node after the machine pauses.
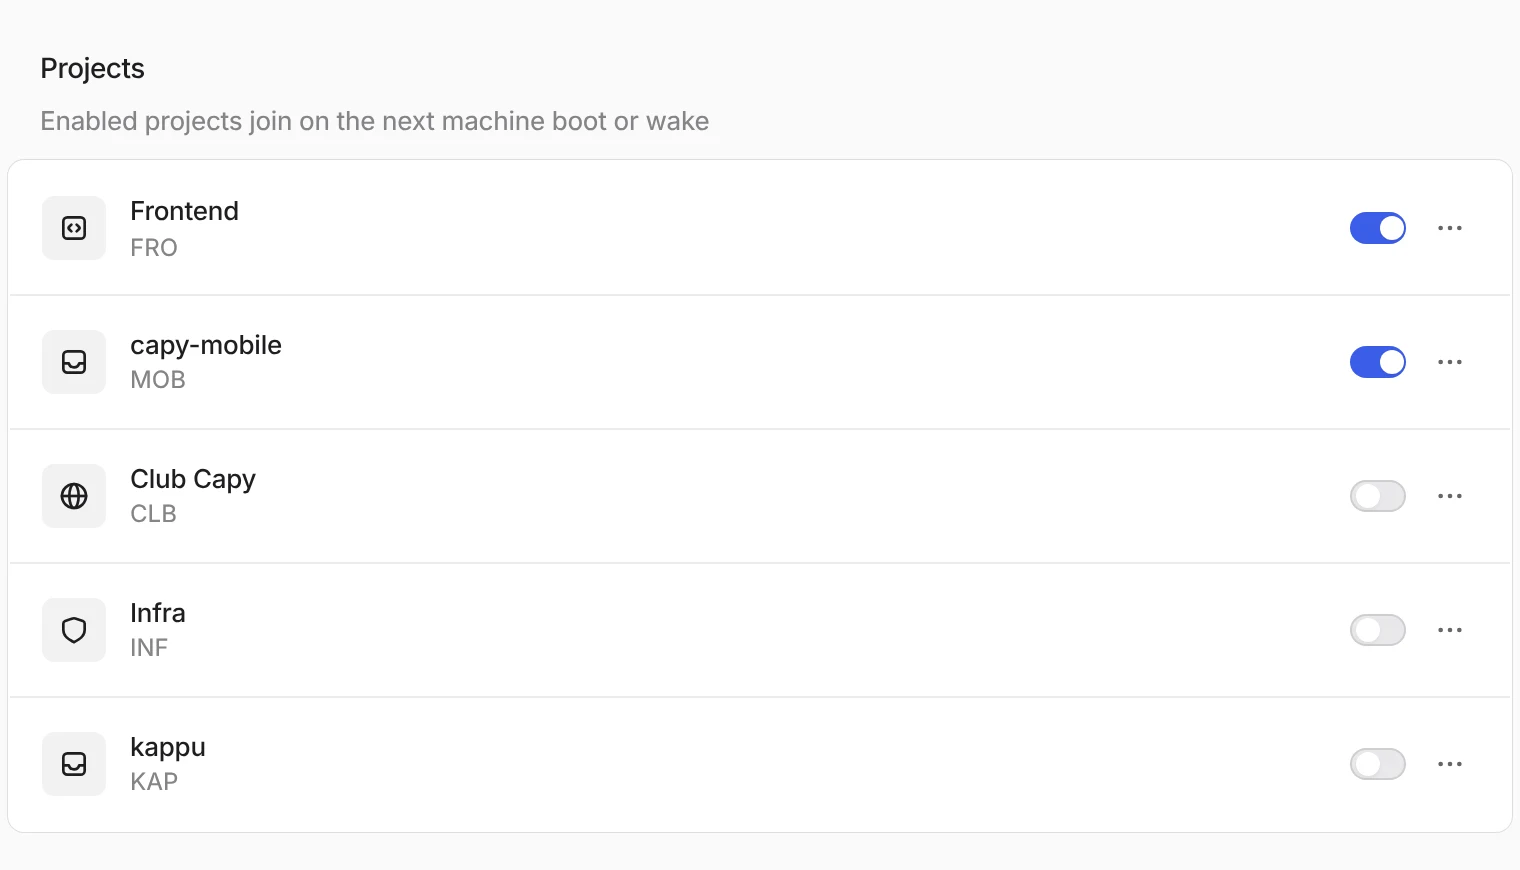
Project by project
Only machines in the projects you turn on join. Machines in other projects never do.
FAQ
Setup, access, keys, and how to cut a machine off.
What do agents get access to?+
Do my services need to be public?+
How are the auth keys handled?+
What happens to nodes when a machine sleeps?+
What if a machine can’t join?+
How do I cut off access?+
How many connections does an organization need?+
Give agents your private network
Connect your tailnet once, and machines in the projects you pick reach the services your tailnet policy grants.